


Policy & Regulation
Infosys CEO Salil Parekh said during an earnings call that the Trump administration's crackdown on US employee immigration programs, including the Permanent Labor Certification Program and H-1B visas, will not materially impact the company's costs or attrition. He noted that the majority of Infosys' US workforce are local hires, a shift underway for several years. The Department of Labor suspended Infosys and four other IT firms from the Permanent Labor Certification Program on Oct. 8. Infosys reported $5.1 billion in Q2 FY27 revenue, 1.5% year-over-year growth in constant currency, and revised its FY27 revenue growth guidance to 1-2%. AI made up 10.5% of revenue, and the company won large deals totaling $5.2 billion.
The California Department of Tax and Fee Administration is finalizing enforcement plans for a sales tax on software-as-a-service products, effective Jan. 1, 2027, following the enactment of Senate Bill 122. The law imposes a state tax on prewritten software, including cloud-based offerings, while exempting custom software and digital infrastructure. Value-added resellers and distributors face at least a 7.25% tax on software sold to end customers, but clarity is lacking on key issues such as resale treatment, optional maintenance agreements, and bundled offerings. Industry groups including the Computer and Communications Industry Association and Salesforce have raised concerns, while some executives downplay the impact as a minor annoyance.
Impartner recently integrated Configure, Price, Quote (CPQ) tools into its Partner Revenue Management Platform to address deal delays in the channel caused by manual processes. This feature allows partners to autonomously create and advance quotes within commercial parameters set by vendors, without needing to route routine deals back to the vendor. This is expected to reduce time and operational costs for deals while enhancing the partner experience.
At DEF CON, the Franklin Project announced a new initiative to fund five channel partners to provide free cybersecurity monitoring services to small U.S. water systems and share threat intelligence through the newly established Water Watch Center. The project aims to address the challenge small water facilities face in coping with cyberattacks due to insufficient staffing and resources.
A coalition of over 100 tech companies and other organizations has proposed a security reporting system for AI agents, aiming to prevent out-of-control models from causing harm to society. The system, named "Shared AI Discovery Exchange" (SAFE), developed by the Open Security AI Alliance working group, will establish mechanisms to collect information on AI-related security incidents, share it with affected organizations, identify commonalities among incidents, and publish recommendations based on lessons learned. The Linux Foundation released the draft for comment on Tuesday.
N-able issued a security update on Monday, stating that a critical vulnerability in its N-central remote monitoring and management platform was exploited over the weekend, and emergency fixes have been deployed. Currently, only a few customers have been breached. The vulnerability stems from a licensing issue that appeared after the latest version released on July 30, affecting both on-premises and cloud deployments. Attackers could remotely access managed endpoints via the Take Control feature. N-able has identified six related IP addresses.
Westcon-Comstor updated its climate commitments last week, targeting a halving of Scope 1 and 2 emissions by 2030. The company has reduced emissions by 42% since fiscal year 2022, with renewable energy accounting for 54%. Facing growth in Scope 3 emissions, the company calls on suppliers and partners to jointly participate, driving value chain decarbonization through dialogue and transparency.
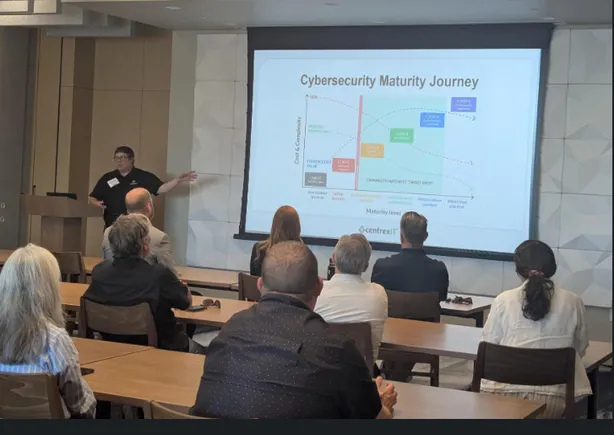
Coalition executives emphasized that its security business is legally separated from its insurance business, protecting customer data through a third-party breach advisor mechanism, and using monthly contracts and tiered discounts to attract MSP partnerships. Josh Hohbein of CentrexIT transformed from a skeptic to a user, validating the effectiveness of this model.
On Monday, the U.S. Department of Defense announced the suspension of the CMMC Phase 2 compliance deadline originally set for November 10, aiming to lower barriers for small innovative enterprises entering the defense industrial base. Certified IT service providers say they do not regret their investment, though some consulting projects face suspension. Industry experts note that CMMC remains a legal requirement, and the need for cybersecurity compliance has not changed.
The Trump administration announced this week the launch of the Gold Eagle project, aimed at coordinating the application of frontier AI models in vulnerability discovery and remediation to address the surge in vulnerabilities caused by AI and pressure on the security community.