


Security
Network management vendor Jamf released a report on Tuesday, based on interviews with 687 IT and security leaders, revealing the correlation between AI adoption and the frequency of security incidents in macOS environments. The report shows that over 20% of organizations have already suffered losses or attacks due to AI tools, and about 60% expect AI-related incidents to occur in the near future. Organizations with deep AI integration have an incident rate as high as 27%, while those in the exploration phase have a rate below 20%. Jamf recommends reducing risks through regular audits, software governance, and early integration of governance frameworks.
Dozens of renowned cybersecurity experts jointly wrote to US Commerce Secretary Howard Lutnick and National Cyber Director Sean Cairncross, criticizing the Trump administration's ban on Anthropic opening its Fable 5 and Mythos 5 models to foreign entities. The experts argue that the export control directive lacks a basis in actual risk, yet weakens defenders' capabilities, creates market uncertainty, and endangers US AI leadership. As of Monday morning, the letter had garnered 76 signatures, including CEOs, CISOs, venture capitalists, and prominent security researchers.
A report released by Netrio on Monday shows that mid-sized enterprises generally expect AI to boost productivity, but challenges such as security, data preparation, and integration complexity are hindering progress. The survey found that 82% of respondents have deployed AI in production, but only 26% have achieved governance at scale. Investment continues to grow, with nearly 90% of enterprises planning to invest at least $100,000 in the next one to two years.
Cybersecurity certification body ISC2 released a report on Wednesday stating that as enterprises prepare for the AI era, security training budgets continue to increase. 47% of respondents believe AI is the most essential skill for employees to master, and 73% of enterprises have raised security training investment over the past year. The report also analyzed training delivery models, frequency, effectiveness evaluation methods, and major challenges.
ServiceNow and IBM announced an expanded partnership on Thursday, combining IBM's AI, data, and automation capabilities with ServiceNow's AI platform to address challenges related to legacy systems and data readiness in enterprise-scale AI deployment. The collaboration focuses on application modernization, enterprise data governance, and autonomous infrastructure operations, with related joint capabilities expected to be available in the second half of 2026.
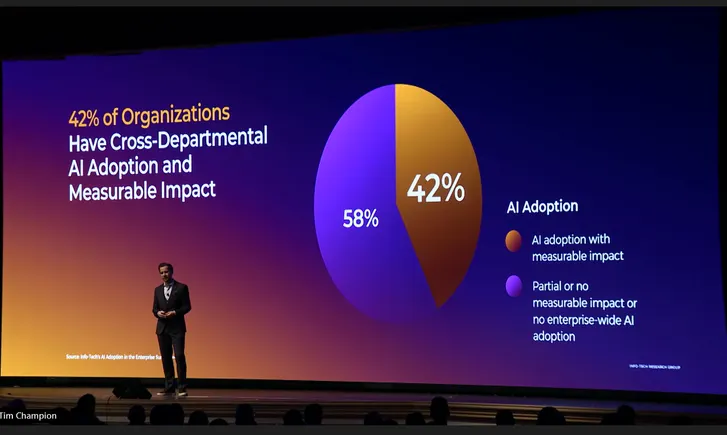
In a keynote address on Tuesday, Info-Tech Research Group CEO Tom Zehren stated that although agentic AI has transformative potential for enterprises, technology leaders such as CIOs still face deployment challenges. He proposed a four-step framework based on surveys and industry research to help technology leaders develop an AI strategy that measures value, and emphasized that security measures, IT budgets, AI strategy, and employee buy-in are key factors.
Outtake's latest report indicates that AI not only enhances hackers' abilities to analyze vulnerabilities and write malware but also poses a serious threat in identity impersonation. This year, 53% of organizations have faced impersonation attacks targeting executives or frontline employees, and 47% have encountered confirmed or suspected synthetic media impersonation incidents. However, 75% of surveyed enterprises only conduct limited monitoring or post-incident response, and only 43% carry out executive identity deception simulations. The lack of oversight for AI agents also poses a hidden risk, with only 4% of enterprises fully monitoring AI agents. Governance fragmentation is widespread, with 21% of enterprises lacking a dedicated team responsible for digital trust risks.
At the Gartner Security & Risk Management Summit, multiple analysts reminded CISOs that, in the face of threats from new AI models such as Anthropic Claude Mythos and OpenAI Daybreak, they should return to security fundamentals, avoid being misled by hype, and be wary of AI investments eroding budgets and talent reserves.
U.S. President Trump established a voluntary review mechanism for frontier AI models through an executive order, with the Department of Homeland Security, the Department of the Treasury, the Office of the National Cyber Director, and NIST tasked to develop standards within 60 days. The order does not impose mandatory licensing, but CIOs should be wary of potential impacts from alternative mechanisms such as the Defense Production Act.
Enterprises are rapidly adopting AI agents, but the resulting security risks and governance issues are drawing attention. Gartner predicts related spending will increase by $6 billion in 2026, while Okta reports that over half of enterprises experienced AI-related security incidents last year. Experts point out that the autonomy of agents requires stricter permission controls, and security responsibility is shifting from the CISO to cross-departmental sharing, with governance and security strategies needing to evolve in tandem.